Why Do Employees Ignore Security Training They've Already Received?
Completing a security awareness session and actually changing daily habits are two different outcomes, and most training programs only measure the first one.
In Simple Terms (For Beginners)
Security awareness training teaches employees to recognise threats like phishing emails, but sitting through a session doesn't guarantee someone changes their behaviour the next time a suspicious email lands in their inbox.
- Employees often complete required training and then revert to old habits within weeks, because attendance was the goal rather than behaviour change.
- Annual, one-off sessions are a weak format for building habits compared to shorter, more frequent reinforcement.
- Training that ties directly to an employee's actual daily tools and tasks sticks better than generic content.
HUMAN FIREWALL · September 24, 2026 · 5 min · By Hardik Patel
Why do employees ignore security training they've already completed? Training is usually delivered once a year as a compliance checkbox, disconnected from an employee's daily work, so the knowledge fades within weeks and doesn't get reinforced at the exact moment a real decision — like whether to click a link — actually needs to be made.
The Gap Between Knowing and Doing
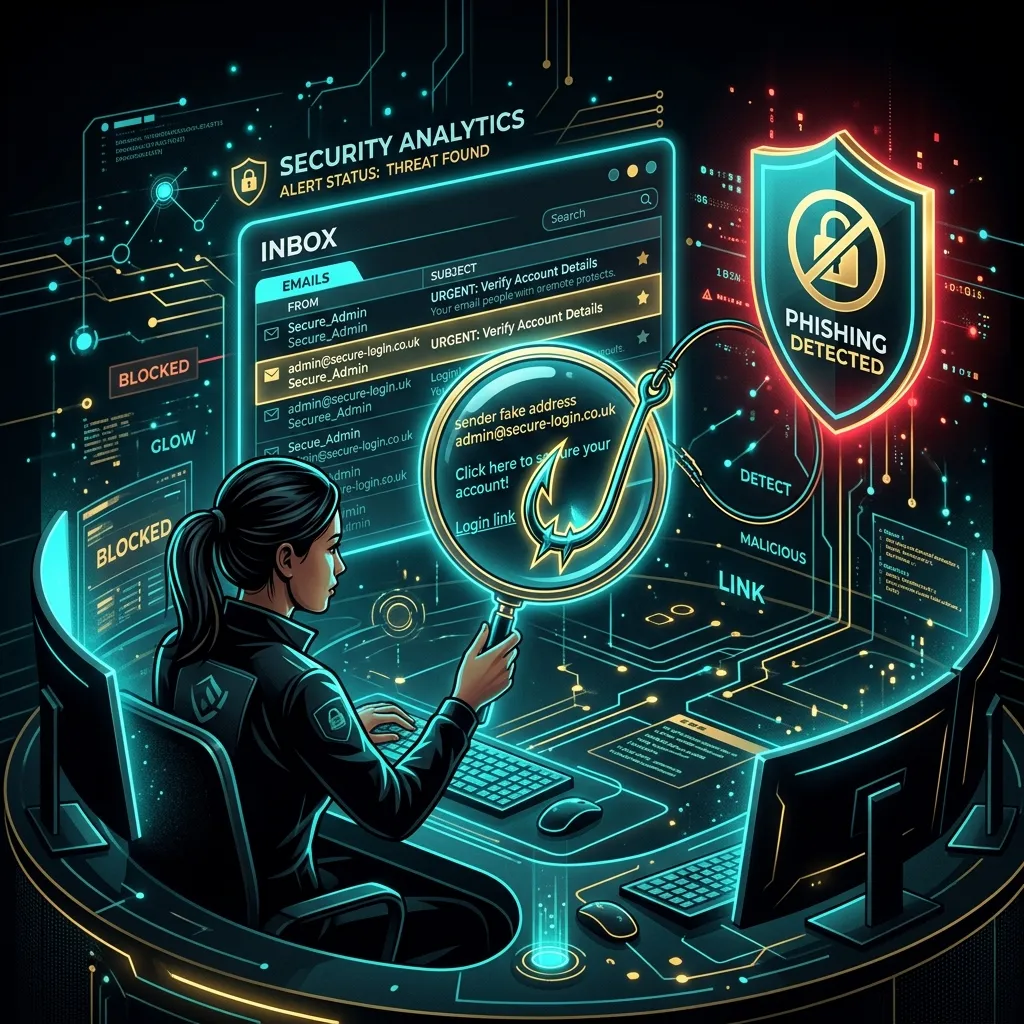
Most employees who complete phishing awareness training can correctly answer questions about it on a quiz immediately afterward. The failure shows up weeks later, when a real email arrives during a busy afternoon and old habits take over.
This isn't a knowledge problem, it's a behaviour problem. Knowing what a phishing email looks like in the abstract is different from pausing to apply that knowledge in the middle of an actual workday.
Training that treats awareness as a one-time information transfer, rather than an ongoing habit to build, tends to produce this exact gap.
Why Annual Training Alone Doesn't Work
A single yearly session, however well designed, competes with eleven months of no reinforcement. Most people forget the specifics of training content within a few weeks without repetition.
Compliance-driven programs often optimise for attendance and a passed quiz rather than measurable behaviour change, because attendance is easier to track and report than actual click rates on real phishing tests.
Shorter, more frequent touchpoints — a five-minute monthly refresher, a quick note after a real attempted scam, a simulated phishing test with immediate feedback — build habits more effectively than a single long annual session.
What Actually Changes Behaviour
Training tied to an employee's real tools and workflow, rather than generic scenarios, transfers better. A finance team benefits more from examples of invoice fraud than from a broad overview covering every threat type.
Immediate, low-pressure feedback matters. An employee who clicks a simulated phishing link and gets a short explanation right away learns more than one who finds out weeks later in an aggregate report.
Making it socially normal to report a suspicious email, without embarrassment for a false alarm, increases how often real threats actually get flagged instead of ignored or quietly deleted.
Key Takeaways
- Passing a training quiz doesn't reliably predict real-world behaviour under normal work pressure.
- Frequent, short reinforcement beats a single long annual session for building lasting habits.
- Training tied to an employee's actual daily tools and role sticks better than generic, one-size-fits-all content.
Frequently Asked Questions
Q: How often should security awareness training actually happen?
A: Short monthly or quarterly touchpoints, combined with periodic simulated phishing tests, tend to produce better real-world results than a single annual session, even if the total training time is similar.
Q: Does punishing employees who fail phishing simulations help?
A: Generally not — it discourages people from reporting mistakes or suspicious emails out of fear, which is the opposite of what a security-aware culture needs. Feedback and coaching work better than penalties.
How iTechFixr Can Help
We design ongoing awareness programs built around short, frequent reinforcement and role-specific scenarios instead of a single annual session, along with simulated phishing campaigns that give employees immediate, judgment-free feedback.
Need Help With This?
Talk to Hardik directly about your organisation's cybersecurity needs — get a tailored response within 24 hours.
